

Adding ACLs to a Server Instance Group or Endpoint Group
To add an ACL to a Server Instance Group or Endpoint Group, first you must have a Private Network or a Pre-created Network set up on your Infrastructure Designer and it must be connected to the Server Instance Group or Endpoint Group. Also select the Network Profile in the Private Network, if required.
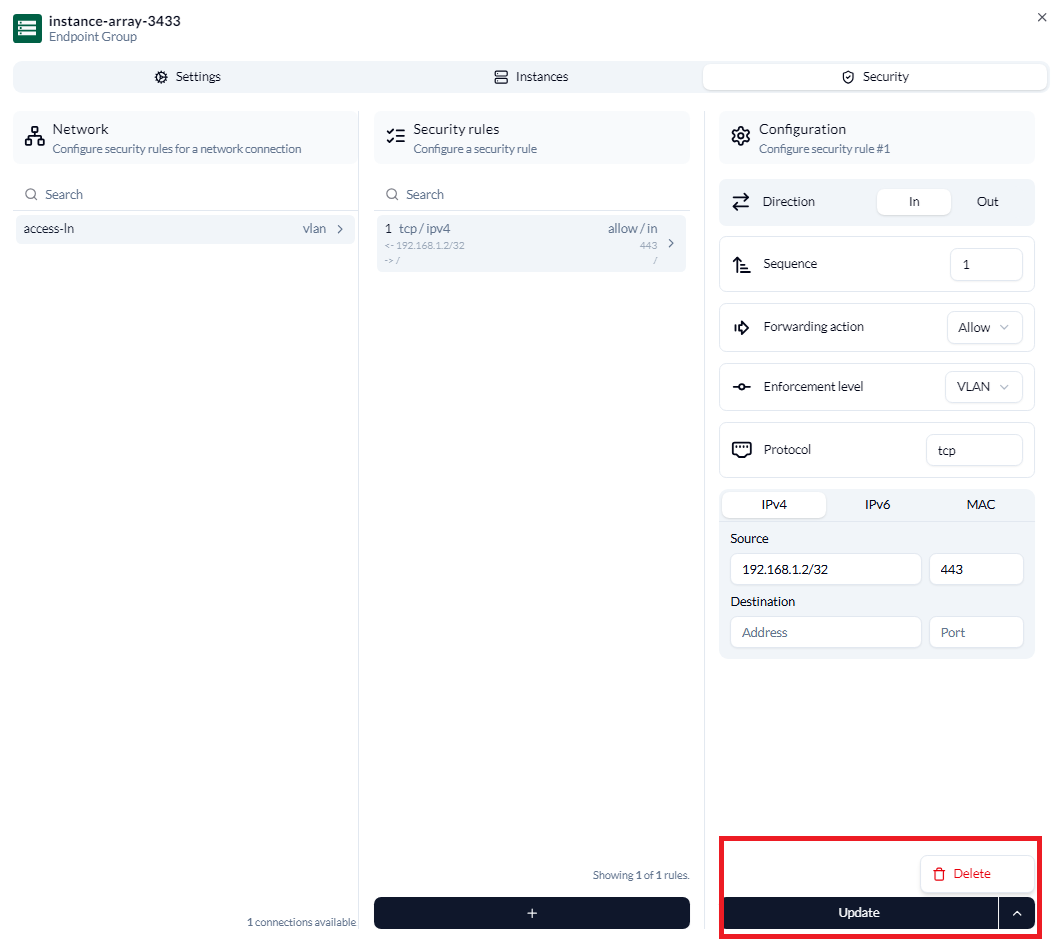
Click the Server Instance Group or Endpoint Group to pop up a window on the right, then click the Security tab and click the network.
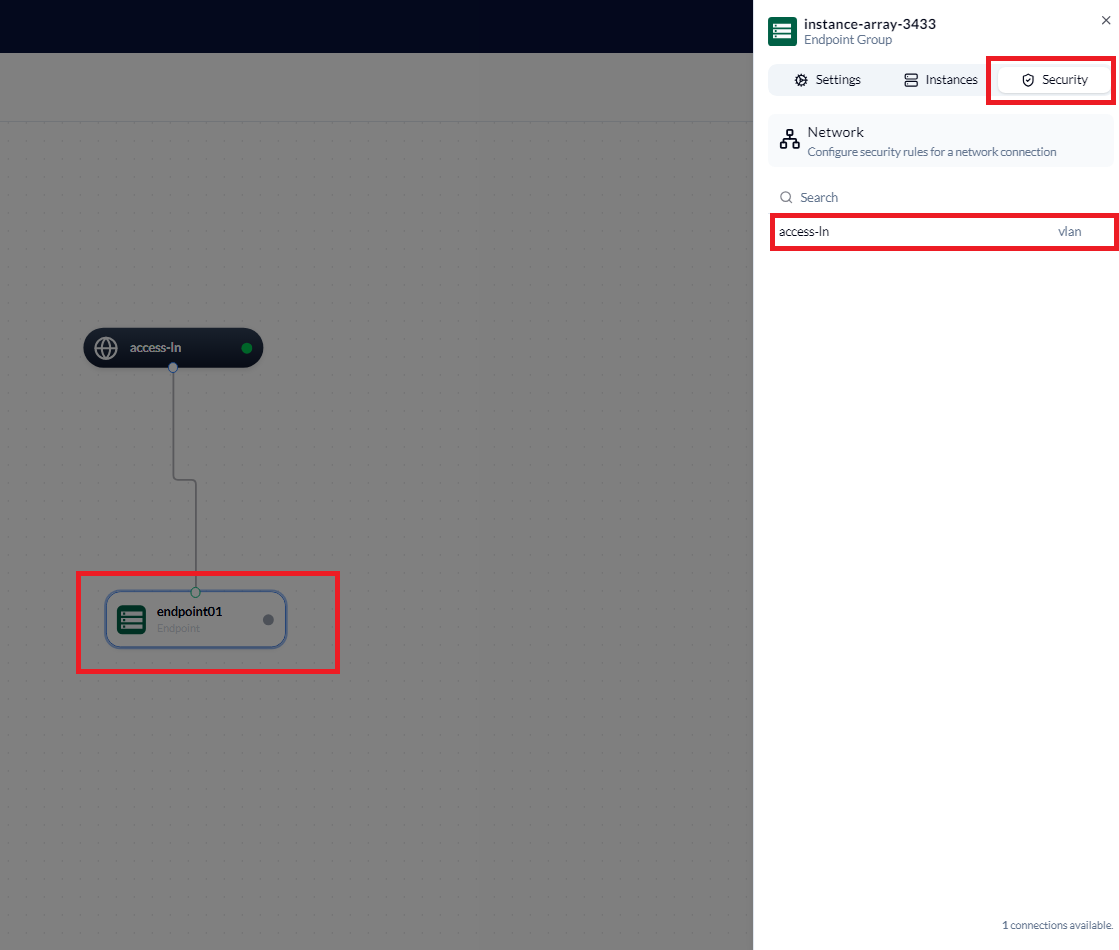
This scrolls out the Security rules for that endpoint and network. Click the + at the bottom of the page.
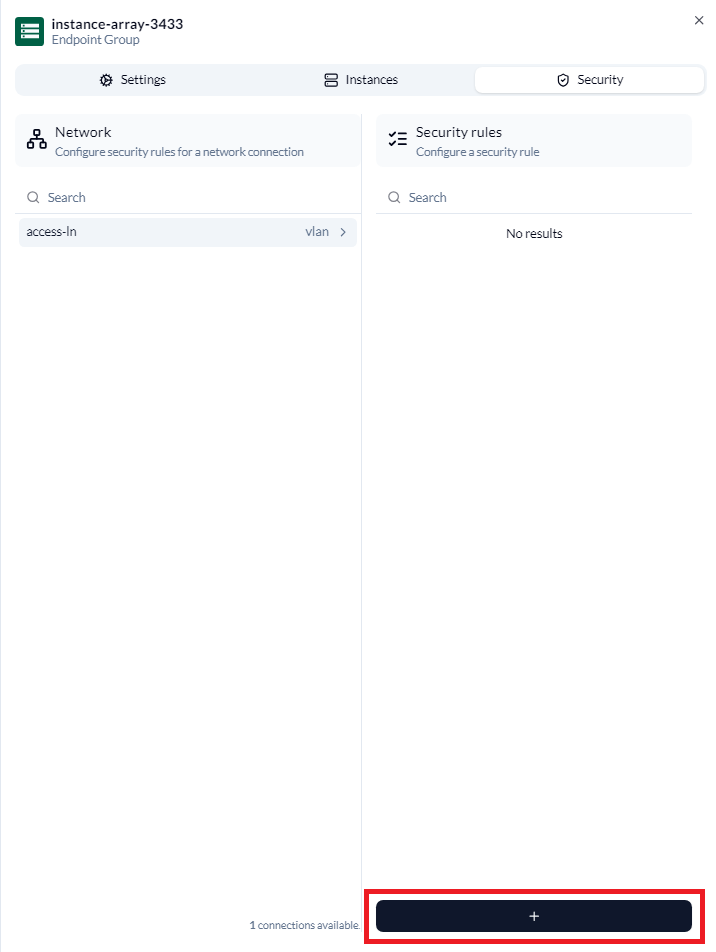
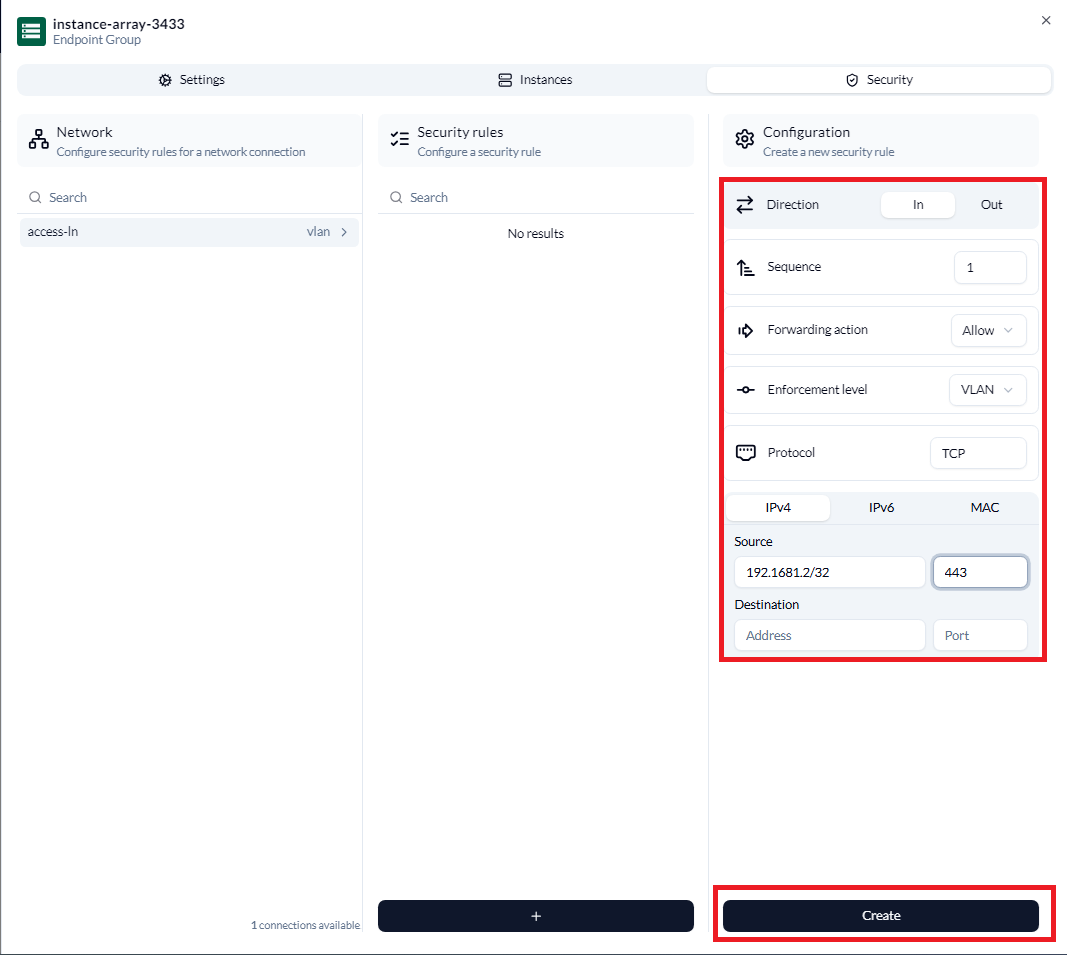
This scrolls out the Security Configuration. Fill in the following:
- Direction - Select between In and Out.
- Sequence - Select a unique priority number.
- Forwarding action - Select Allow, Deny, Discard, or Transit.
- Enforcement level - Select VLAN or Physical Interface.
- Protocol - Type in TCP or UDP as required.
- IPv4/IPv6/MAC - Select whether to use IPv4, IPv6, or MAC address.
- Source - Fill in if required. Example Address 192.168.1.2/32. Example Port 443.
- Destination - Fill in if required. Example Address 192.168.1.2/32. Example Port 443.
Click Create.
MetalSoft returns you to the previous stage, where the new rule appears. Click the rule to modify it. Click Update once complete, or click the arrow next to Update and click Delete if the rule is no longer required.
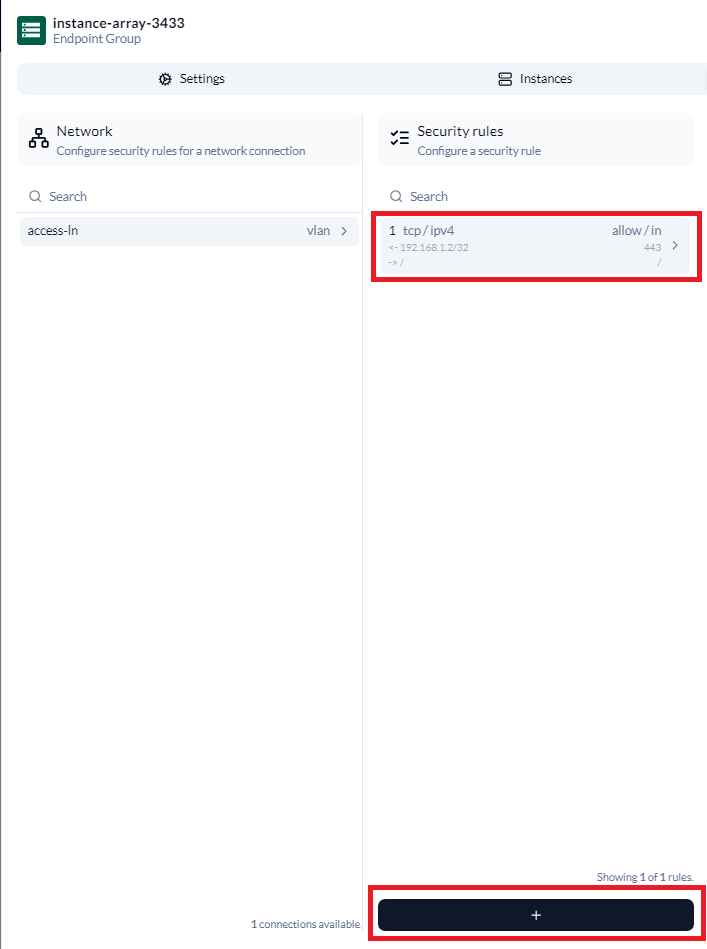
Click + at the bottom to add another rule.